Secure SDLC without slowing delivery
Security that lives in the pipeline instead of at the end of it. Five controls that catch most of what matters…
Cloud platforms, remote work, connected devices, and third-party tools create more entry points for attackers.
Modern attacks use AI, automation, and advanced techniques to bypass traditional security controls.
Without centralized monitoring, suspicious activity can remain hidden until it becomes a serious incident.
Delayed detection and unclear response processes can increase downtime, damage, and recovery costs.
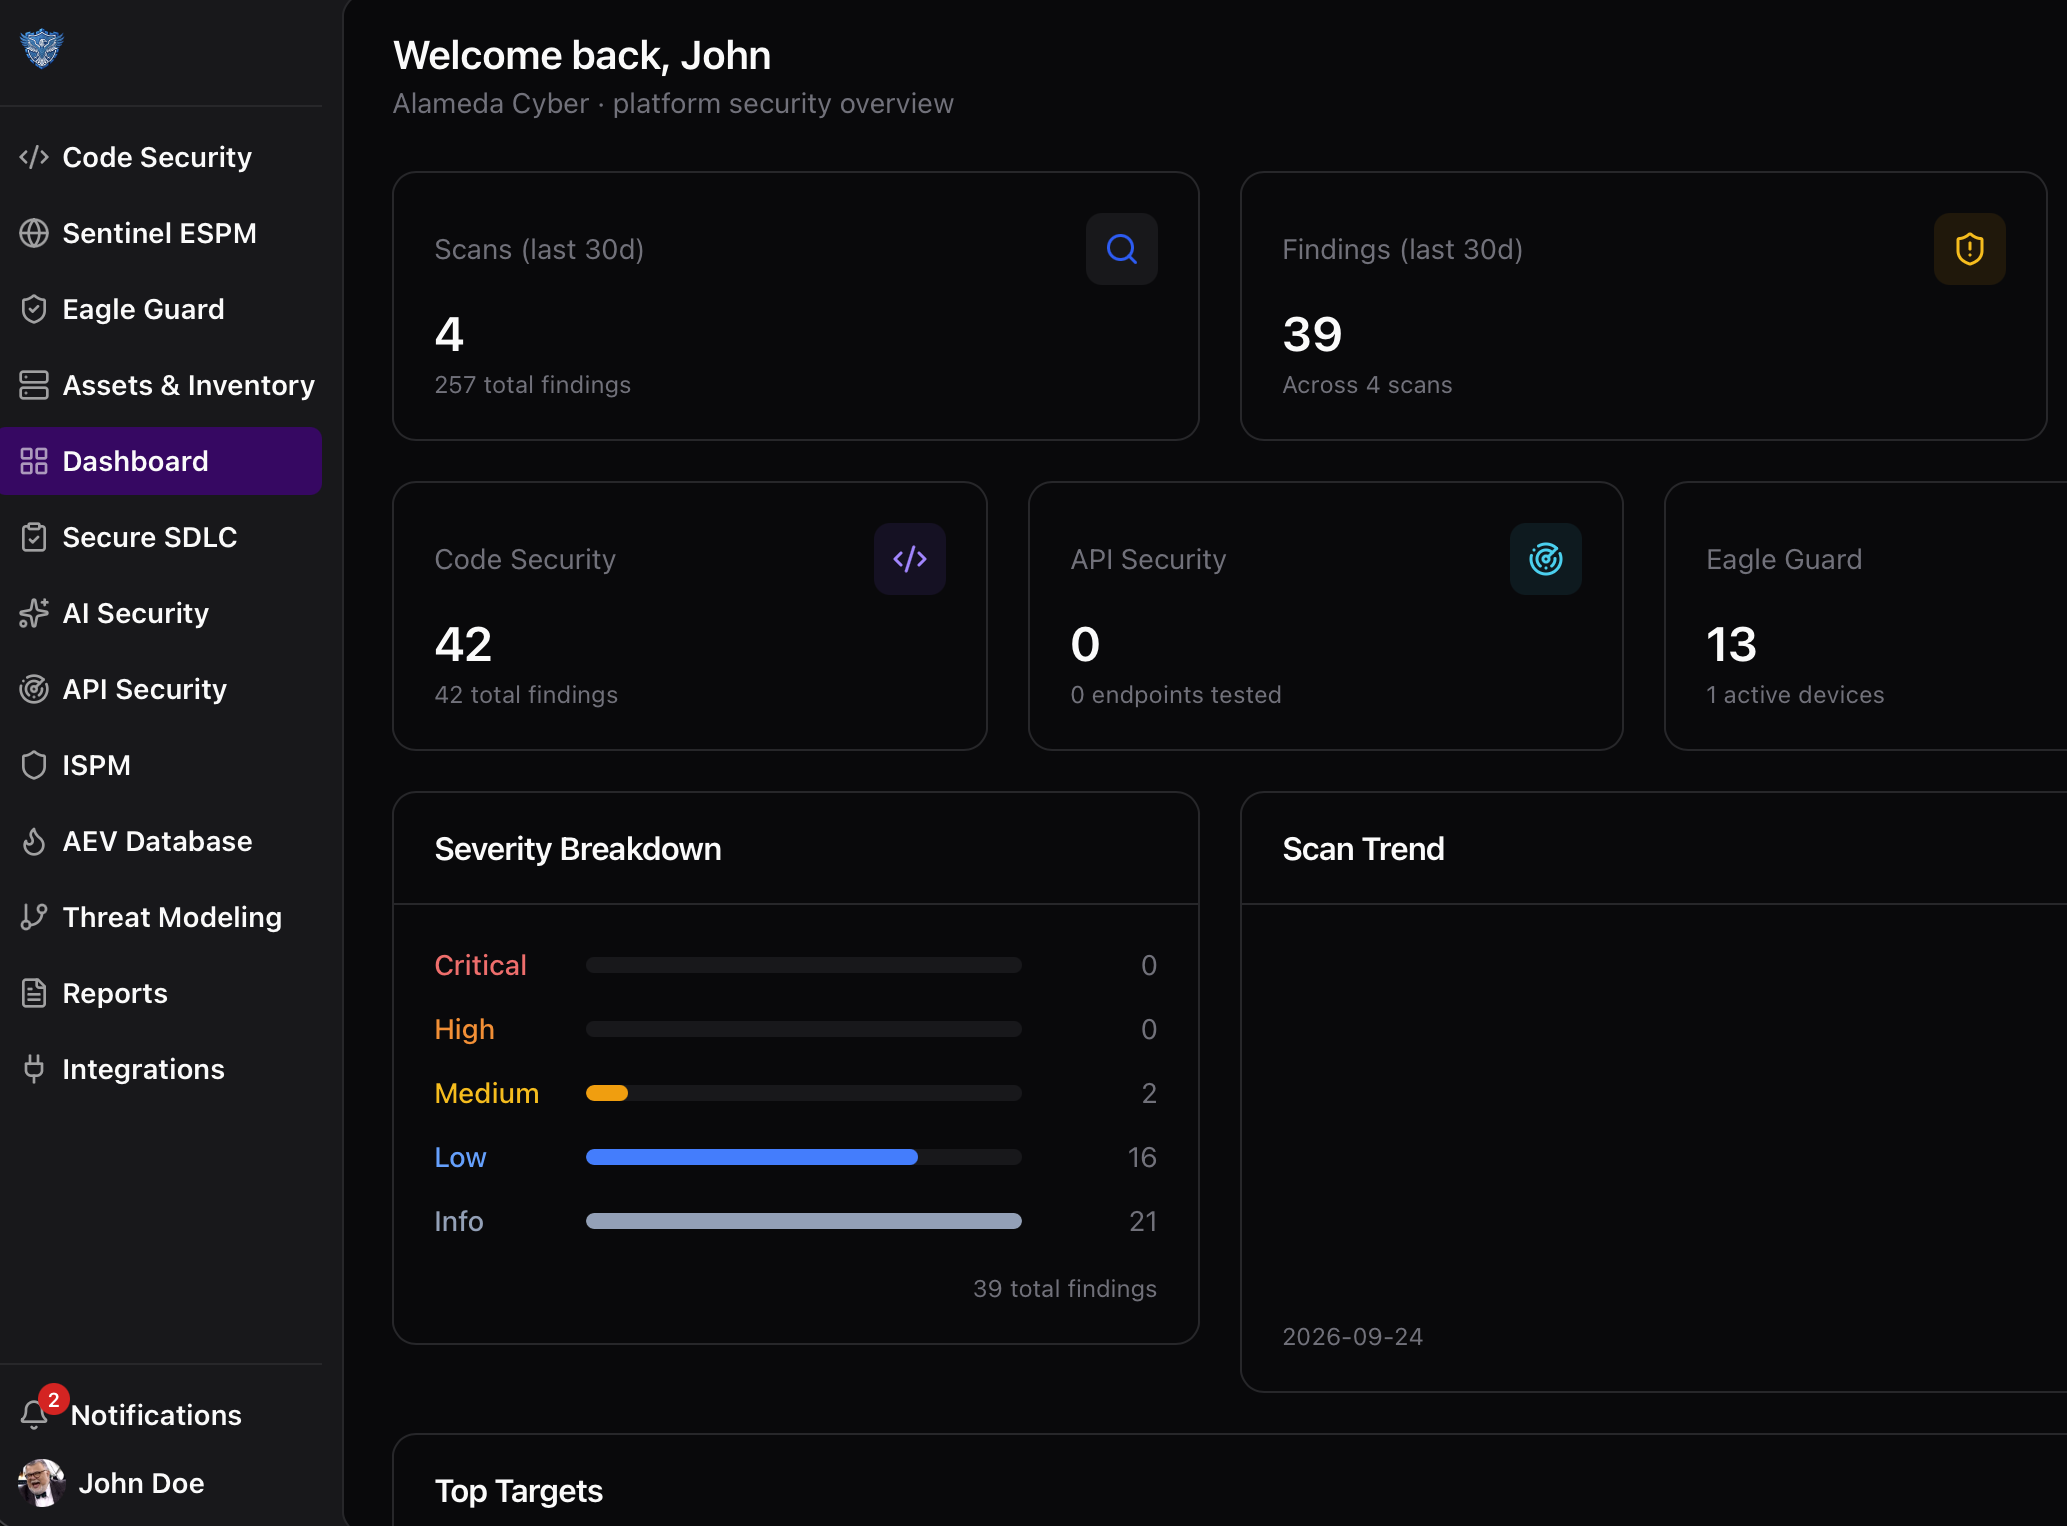
EagleWise brings Secure SDLC, application security, and exposure management into one platform. It reports what you connect and what is already public.
Code Security reads the repositories you connect — dependencies, secrets, static analysis — and API Security checks the APIs you designate. Every finding comes with an owner.
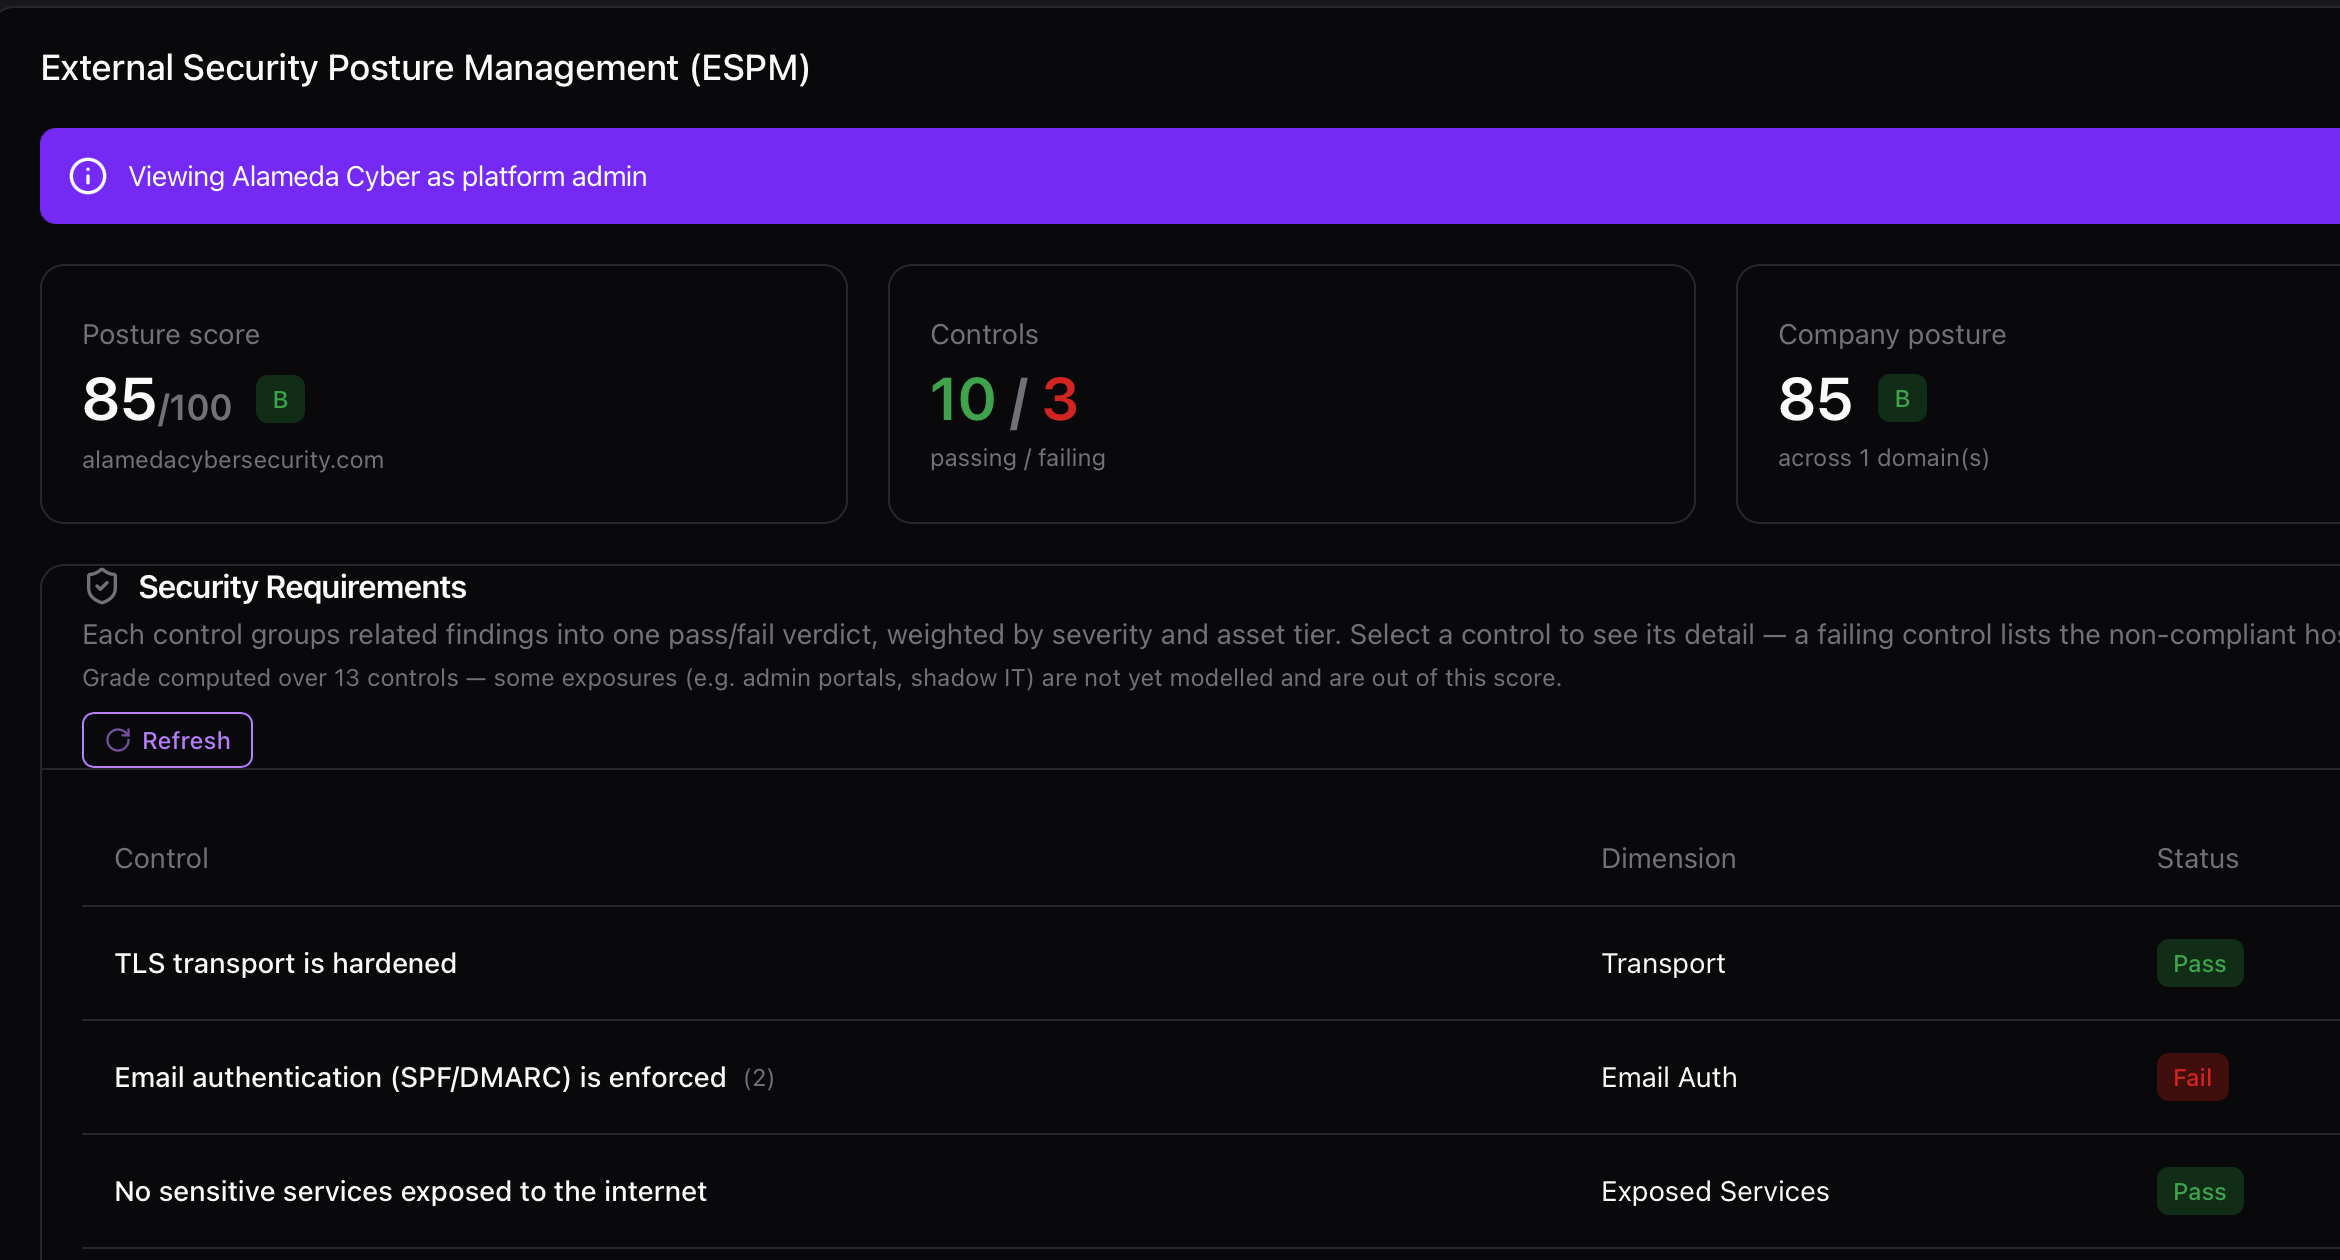
Sentinel builds the outside-in view of what is already public — names, services, certificates, leaked credentials — and alerts you when it changes.
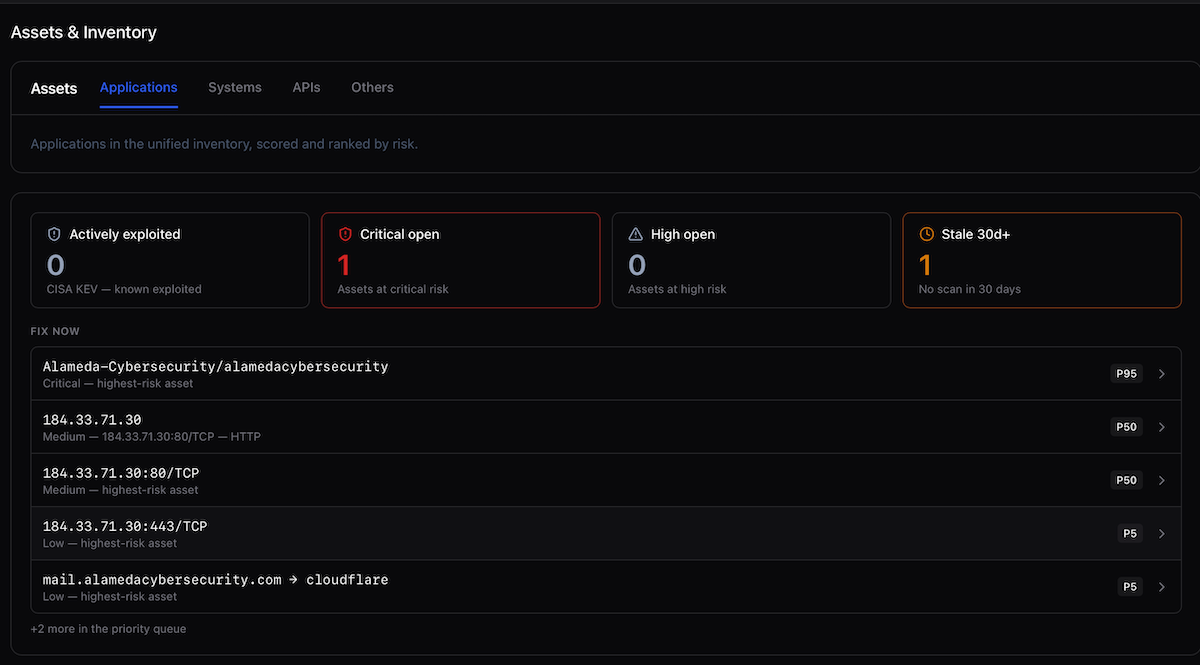
Findings are ranked by reachability and impact, set beside known-exploited issues, and routed to the team that owns the code or the system.
Sentinel and Eagle Guard alert your team, and integrations carry alerts into your SIEM or ticketing. Your team owns the incident: EagleWise alerts, Alameda does not staff, contain or recover it.
Informational: tracked, nothing to do now.
Fix in the normal release cycle.
What changed since the last scan
Reachable weakness: fix before the next release.
Exploitable exposure on a public system: fix now.
Alerts are distributed across multiple dashboards, making critical activity difficult to identify quickly.
Scan results sit in inboxes and spreadsheets; no ticket, no owner, no date.
Analysts lose valuable time moving between communication, monitoring, cloud, and ticketing platforms.
The same weakness is found again next quarter because nothing carried it to the team that could fix it.
Multiple disconnected tools and limited visibility
Exposure changes and device events go to your SIEM, Slack or email.
Jira and ServiceNow tickets are created and updated from findings, with the owner already set.
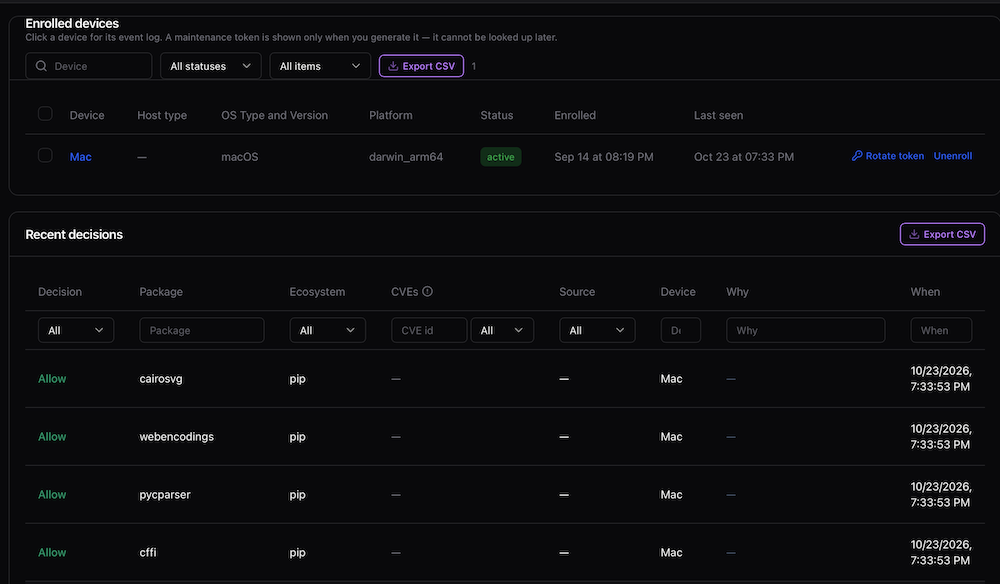
Code findings, exposure, assets and enrolled devices in one view, so a finding is read next to what it affects.
EagleWise alerts and keeps the map current. Alameda does not staff, contain or recover incidents — that stays with your team.
One connected, automated cybersecurity workflow
Security that lives in the pipeline instead of at the end of it. Five controls that catch most of what matters…
Attackers do not start from your CMDB. They start from DNS, certificates and the open internet…
The first hour of a security incident is decided months earlier. A practical plan for teams that ship software…
Alameda, California 94502, USA